Researchers have uncovered what may be the first known case of a zero-click spyware attack. The operation is linked to an Israeli advertising organization that allegedly abused online ads to reach a prominent international media company based in Qatar.
Citizen Lab, a research unit at the University of Toronto, investigated a large-scale covert effort to install spyware through online advertising. The unit named the technique AdFection. Unidentified Israeli actors allegedly used it to infect computers belonging to Al Jazeera's news network.
Citizen Lab said the research is the first public confirmation that zero-click spyware attacks are possible and are already being used in malicious operations. Discover-Tech, an Israeli advertising company, allegedly used AdFection to help spread spyware or carry out other malicious activity.
How Controlium identifies and infects targets
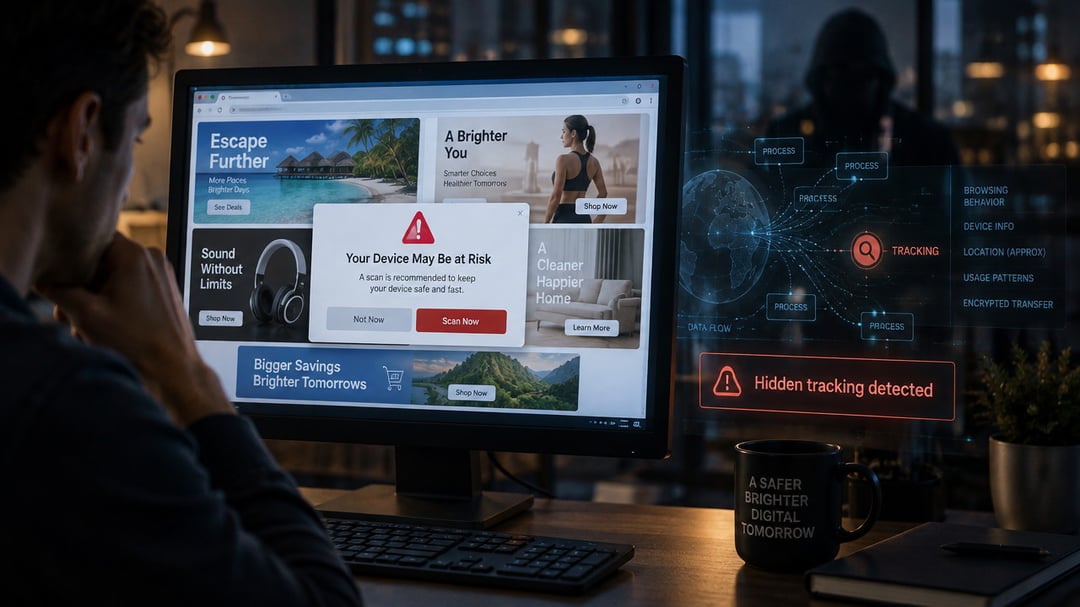
Discover-Tech provides a platform called Controlium. Advertising partners can allegedly abuse it to de-anonymize people and identify selected targets. Controlium also works as a doorway through which third parties can potentially infect computers.
No specific user interaction is required. The platform can allegedly download and run a malicious tool such as Candiru, a commercial spyware product. Citizen Lab found Candiru on Al Jazeera's machines.
Reach across websites, apps, and countries
Discover-Tech's advertising was served across approximately 200,000 unique websites and mobile apps in multiple countries. The ads were designed to direct millions of users to servers associated with Candiru. That tracking and reconnaissance operation was then used to identify and infect selected targets.
Discover-Tech is listed among Google's "certified" advertising vendors. It is also described as a GDPR-compliant company operating in European countries.
Dark Cartographer and the advertising vendors
Citizen Lab identified a second threat actor, called Dark Cartographer, that was working with the Israeli advertising platform. The group was mainly interested in exploiting security vulnerabilities affecting mobile carriers, with the aim of de-anonymizing internet users on a large scale.
Citizen Lab researcher Wolfie Christl said major advertising vendors and corporations appeared uninterested in detecting or preventing abuse by malicious Israeli actors. Christl said the entire online advertising ecosystem should now be considered a security threat to governments, private organizations, and ordinary users.
Precision targeting and calls for investigation
The Canadian report documents a malicious technique that researchers have long considered a potential cybersecurity threat. AdFection can be used to identify and compromise specific targets with considerable precision. The report says authorities around the world should investigate the operation and consider appropriate legal action against those responsible.